PHP2Shell: what vendors reported on their status pages, 21 to 23 October 2026
Data read from Third Party Index on 24 October 2026.
Summary
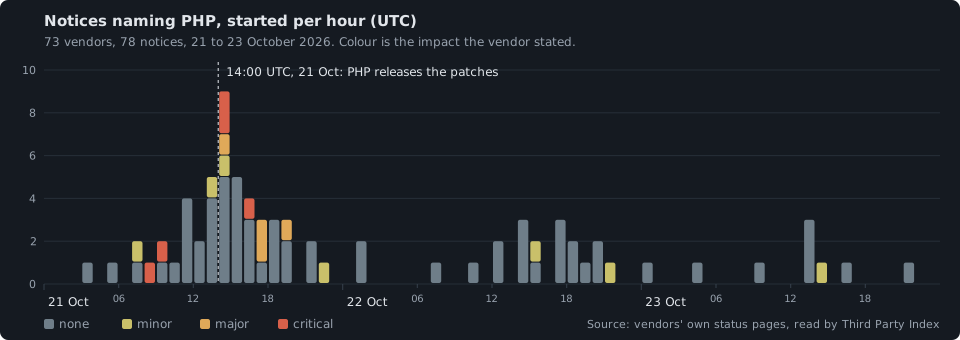
PHP patched two critical remote code execution flaws on 21 October 2026, a day after the details leaked: CVE-2026-109618 and CVE-2026-109619, nicknamed PHP2Shell. Over the next three days, 73 tracked vendors put up 78 incidents or notices on their own status pages naming PHP or one of the CVEs. 62 say no impact. Nine are rated major or critical by the vendor, five of them hosting providers. Posts peaked at 14:00 UTC on 21 October, the hour PHP's patches shipped.
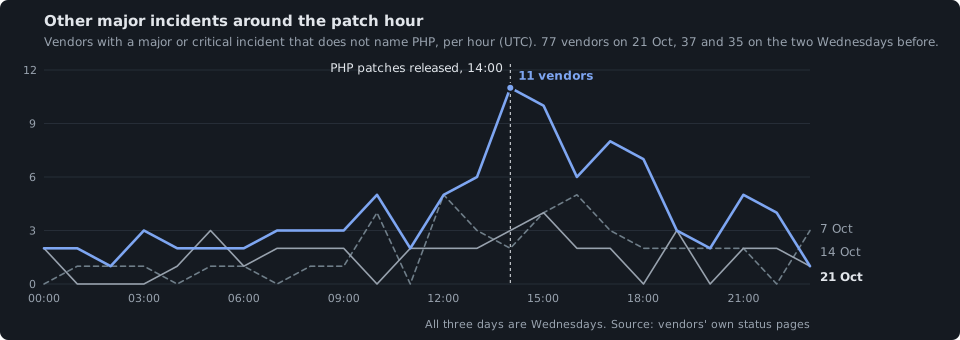
The same day, 77 vendors started a major or critical incident that doesn't name PHP. That's more than double a usual Wednesday, and it peaked in the same hour. A few say they were doing security maintenance. For the rest, nothing public ties them to PHP, and vendors that show PHP on their homepage aren't any more common among them than usual.
All of this is what vendors reported on their own pages. A "not affected" notice doesn't prove a vendor was safe, and "critical" is the vendor's own label. We don't know who was attacked.
The vulnerability
- Two unauthenticated remote code execution flaws in the PHP runtime. CVE-2026-109618 is memory corruption when PHP runs out of memory while setting up a request. CVE-2026-109619 is stale global state that the next request on the same worker can act on (a use-after-free). PHP's security team rates both CVSS 9.2 and says the risk is highest under Apache mod_php, where an exploit was demonstrated.
- Fixes: PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35, released 21 October 2026 at 14:00 UTC. PHP 7.4, 8.0 and 8.1 get no official release (source backports exist), and 7.3 and older get nothing. PHP says no configuration change fully mitigates the flaws, and workers have to be restarted after updating.
What vendors reported
We read incidents from 2,033 status pages and counted every one started between 19 and 24 October whose title names PHP or either CVE.
- 78 incidents or notices at 73 vendors (Hostinger and Hosting24 share a status page).
- The first started 21 October at 03:43 UTC and the last 23 October at 21:24 UTC: 49 on the 21st, 20 on the 22nd, 9 on the 23rd.
- Impact the vendor stated: 62 none, 7 minor, 4 major, 5 critical.
- Status now: 45 resolved, 24 monitoring, 4 identified, 5 investigating.
- Time to resolve: 9 of the 45 resolved ones were posted already resolved (one update, no duration). For the other 36, the median is 6.4 hours and the 90th percentile 26.4 hours.
- At least 10 titles say not affected, no impact or no action needed.
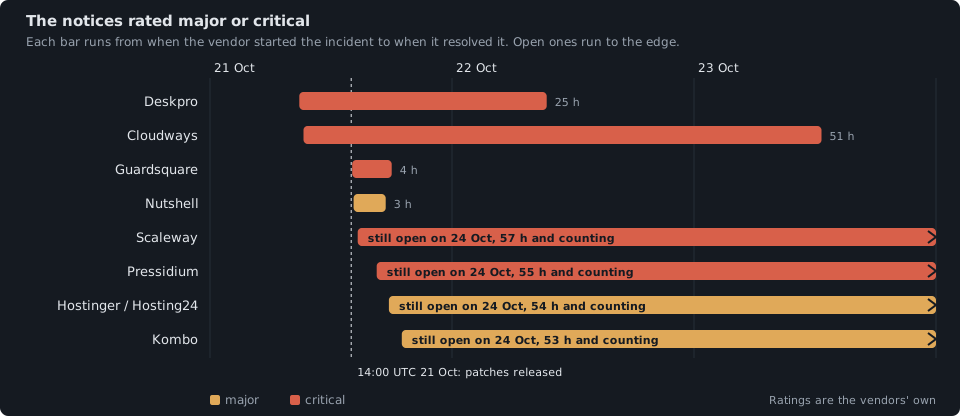
The nine rated major or critical
| Vendor | Rating | Title (vendor's own) | Status |
|---|---|---|---|
| Deskpro | critical | Security vulnerabilities in PHP (CVE-2026-109618 and CVE-2026-109619) | resolved after 24.5 h |
| Cloudways | critical | Critical PHP Remote Code Execution Vulnerabilities - Monitoring & Mitigations Underway | resolved after 51 h |
| Guardsquare | critical | Preventive measures against (CVE-2026-109618 & CVE-2026-109619) | resolved after 4 h |
| Nutshell | major | PHP2Shell Response | resolved after 3 h |
| Scaleway | critical | P2 - [WEBHOSTING] - PHP Emergency maintenance | identified, open |
| Pressidium | critical | Emergency PHP Security Maintenance: Multiple Regions | monitoring, open |
| Hostinger / Hosting24 | major | PHP Security Update for Web, Agency and cPanel Hosting | monitoring, open |
| Kombo | major | Some integrations offline due to php2shell | monitoring, open |
Only Kombo's title reports a service offline. The rest describe emergency maintenance or mitigation.
Patching had its own incidents
Cloudways posted "PHP Security Patch Update: Known Regressions". Scaleway posted "[BookMyName] PHP emergency migration - multiple service regressions" and "Security updates applied to PHP and Node.js runtimes". Kinsta posted "Information in regards to newly discovered PHP vulnerability CVE-2026-115560 (Oct 23, 2026)". We found that identifier nowhere else, so treat it as unconfirmed.
Who posted
Hosting and platform providers: Cloudways, Kinsta, Pressidium, Pagely, Scaleway, Hostinger, Hosting24, Automattic, GoDaddy, Aptible, Servd, amazee.io and Cyso. SaaS vendors that run PHP: Deskpro, Nutshell, Knak, Mews, Picqer, Akeneo and Formstack. And a big group saying they were checking or not affected, including HubSpot, Zapier, Pipedrive, Amplitude, Chargebee, Notion, Akamai, Cloudinary, Staffbase, Instructure and Kaseya.
Who depends on them
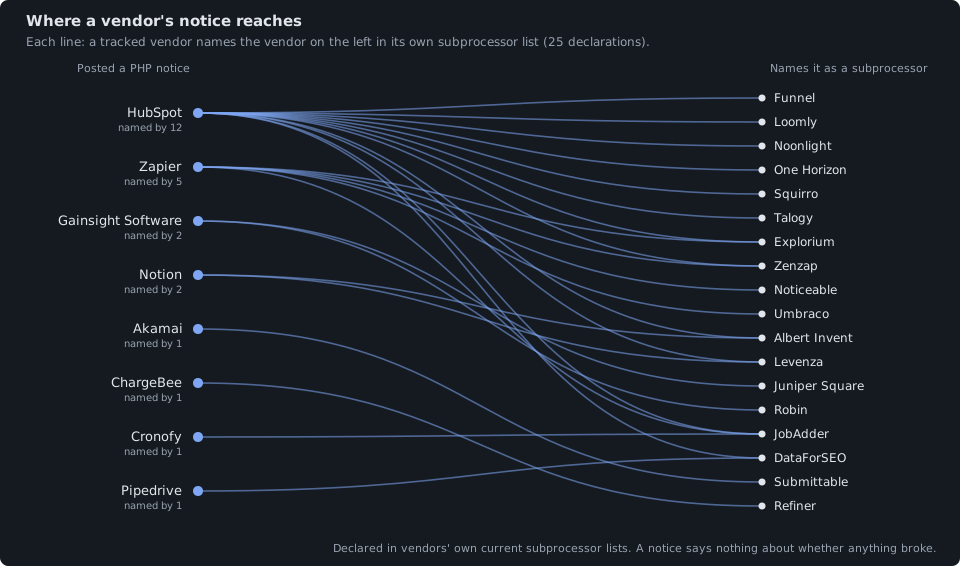
Eight of the vendors that posted are named as a subprocessor by other tracked vendors. 18 tracked vendors name at least one of them, 25 declarations in all, from the vendors' own current subprocessor lists.
| Vendor that posted | Named as a subprocessor by |
|---|---|
| HubSpot | 12 tracked vendors |
| Zapier | 5 |
| Notion | 2 |
| Gainsight | 2 |
| Pipedrive, Akamai, Cronofy, Chargebee | 1 each |
HubSpot, Zapier, Pipedrive, Chargebee and Akamai all posted informational notices (impact none). The list shows where a notice reaches. It doesn't say anything broke.
Context: the whole week was busy
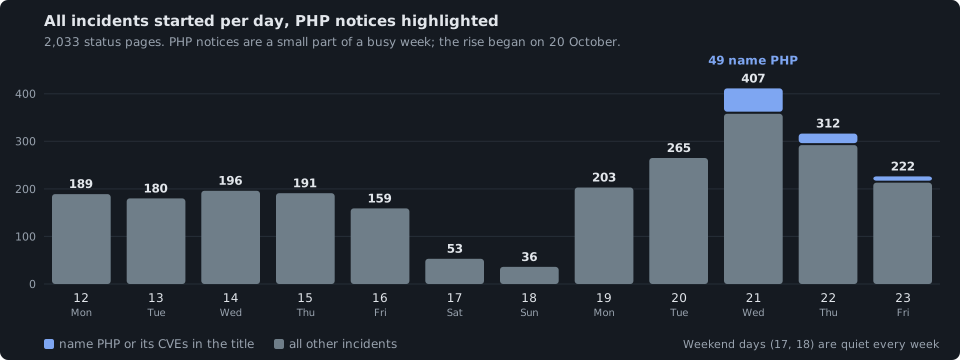
Across all 2,033 status pages, weekdays from 12 to 19 October saw 159 to 203 incidents a day. Then 265 on the 20th, 407 on the 21st, 312 on the 22nd and 222 on the 23rd. PHP notices are 49 of that 407. The other 358 don't name PHP, and the rise started on the 20th, before the patches, so PHP explains only a small part of it. Other security notices on the same days, going by title only: an F5/NGINX advisory, a certificate-authority issue (eMudhra/emSign), Node.js security updates and a LiteLLM supply-chain compromise.
Major incidents that started around the same time: could they be related?
A few vendors say they were doing security maintenance. For most, nothing public connects them to PHP. That day had far more major incidents than usual, and our data doesn't show why.
On Wednesday 21 October, 77 vendors started a major or critical incident whose title doesn't name PHP (121 incidents). The two Wednesdays before had 37 and 35 vendors (45 and 39 incidents). The count peaked at 11 vendors in the 14:00 UTC hour, when PHP's patches shipped, and was 10 in the next hour. Earlier Wednesdays never passed 5 in any hour.
Do they cluster at vendors that run PHP?
Our homepage scans show PHP on 1,506 of 5,193 vendors (29%). Of the 71 scanned vendors with such an incident in the 24 hours from 06:00 UTC on 21 October, 20 (28%) show PHP. On the earlier Wednesdays it was 36% (7 October), 39% (14 October) and 24% (30 September). So no more than usual. It's a weak test: a homepage scan only sees the front end, and not seeing PHP proves nothing.
What the individual cases show
We went through the major and critical incidents from 06:00 UTC on 21 October to 06:00 UTC on 22 October and grouped them by what each vendor's title and our records support.
| Group | Vendors and times (UTC) | What the titles say |
|---|---|---|
| Security maintenance, PHP not named | Exact, three products (11:58 to 12:08), Watermark Insights Tk20 (12:47), EmailOctopus (13:24, critical), WeVideo PlayPosit (13:31), LumApps (14:01) | "Security precaution: ... temporarily unavailable", "Temporarily Offline as a Security Precaution", "Short maintenance to install a security update", "Temporarily Unavailable for Urgent Security Maintenance", "Preventive security maintenance". These fit PHP2Shell and any other security update equally well. |
| Posted its own PHP notice, then had a separate incident | Automattic (PHP notice 14:00; incidents 14:29, 14:35), Granicus (PHP notice 13:54; incident 15:31, critical), Scaleway (14:06, 14:37), Pressidium (PHP maintenance from 16:31; incident 20:08, critical) | "Edge Services Disruption", "Jetpack API is Down", "Temporary Service Unavailability", emergency maintenance on BookMyName and the Dedibox console, "Dashboard Unavailable". Each came after the vendor's own PHP notice or maintenance. Timing makes a link plausible, but no title states one. |
| Posted a PHP notice, incident looks unrelated | Staffbase (09:52), Instructure (21:06), Veritone (19:44), Notion (03:23 on 22 October) | Staffbase's availability incident started five hours before its PHP notice, which said no impact. The others' titles describe something else: Canvas Data 2 errors, US Gov-2, an MCP tool unavailable. |
| Another cause is visible | Ashby (14:31), Ironclad (15:05), Workable (15:08), SalesRabbit (15:24) | Each names a third-party e-signature service (Dropbox Sign) as the source. |
| Nothing connects them | Craft CMS (16:05), SugarCRM (16:09), Improve Digital (13:01) and the rest | Craft CMS: API and plugin store down. SugarCRM: identity login. Improve Digital: creative CDN down, with PHP 7.4.28 seen on its homepage, a branch PHP issued no official fix for. Running PHP and having an incident on the same day doesn't make a link. |